ECC encryption, or Elliptic Curve Cryptography, is predicated on mathematical algorithms governing the algebraic construction of elliptic curves over finite fields. It provides equivalent levels of cryptographic power as RSA and DSA, with a lot shorter key lengths, lowering reminiscence usage and bandwidth calls for. ECC offers faster efficiency, especially on mobile and IoT devices.
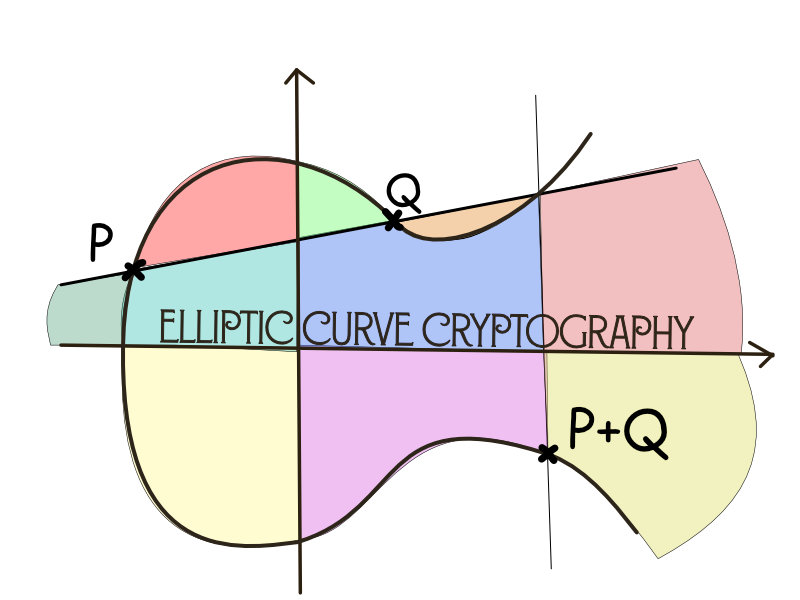
Elliptic Curve Cryptography
Requirements organizations just like the CA/Browser Forum outline baseline necessities for supported key sizes and algorithms to maintain belief and interoperability throughout techniques. ECC is utilized in both digital signatures by way of Elliptic Curve DSA (ECDSA), and in key trade through Elliptic Curve Diffie-Hellman (ECDH). These algorithms are utilized in different parts of the SSL commonplace. First, SSL certificates can be signed with ECDSA instead of RSA. The second use for ECC is during the handshake when the Web server and consumer are negotiating session keys which are used to encrypt all the knowledge sent between the server and browser.
In addition, ECC requires much less processing energy (CPU) and reminiscence, resulting in significantly quicker response instances and throughput on Web servers when it is in use. Performs a key trade operation using the offered algorithm withthe peer’s public key. An elliptic curve non-public key to be used with an algorithm similar to ECDSA.
Why Did Satoshi Select Secp256k1?
We double again and see the last bit is ready, so the original level $P$ is added in. So multiplication is computed utilizing a double and add algorithm, but consists of including two points at each step. It is both the identical two points which is a doubling, or the outcomes of a earlier doubling and the unique point.
Elliptic Curve Cryptography
When encoding the publickey the encodings (PEM,DER) andformat (SubjectPublicKeyInfo)are chosen to outline the exact serialization. When encoding the pointthe encodingX962should be used with the codecs https://objavlenie.com/category/investment (UncompressedPointorCompressedPoint). Encoding (PEM orDER),format (TraditionalOpenSSL,OpenSSHorPKCS8)and encryption algorithm (such asBestAvailableEncryptionor NoEncryption)are chosen to outline the exact serialization. For most applications the shared_key should be passed to a keyderivation operate.
- In libica, an ECDSA signature has always a fair size, and r is given by the primary half, and s by the second half of the signature.
- These operations are the building blocks of elliptic curve cryptography, and are used for producing public keys and signatures in ECDSA.
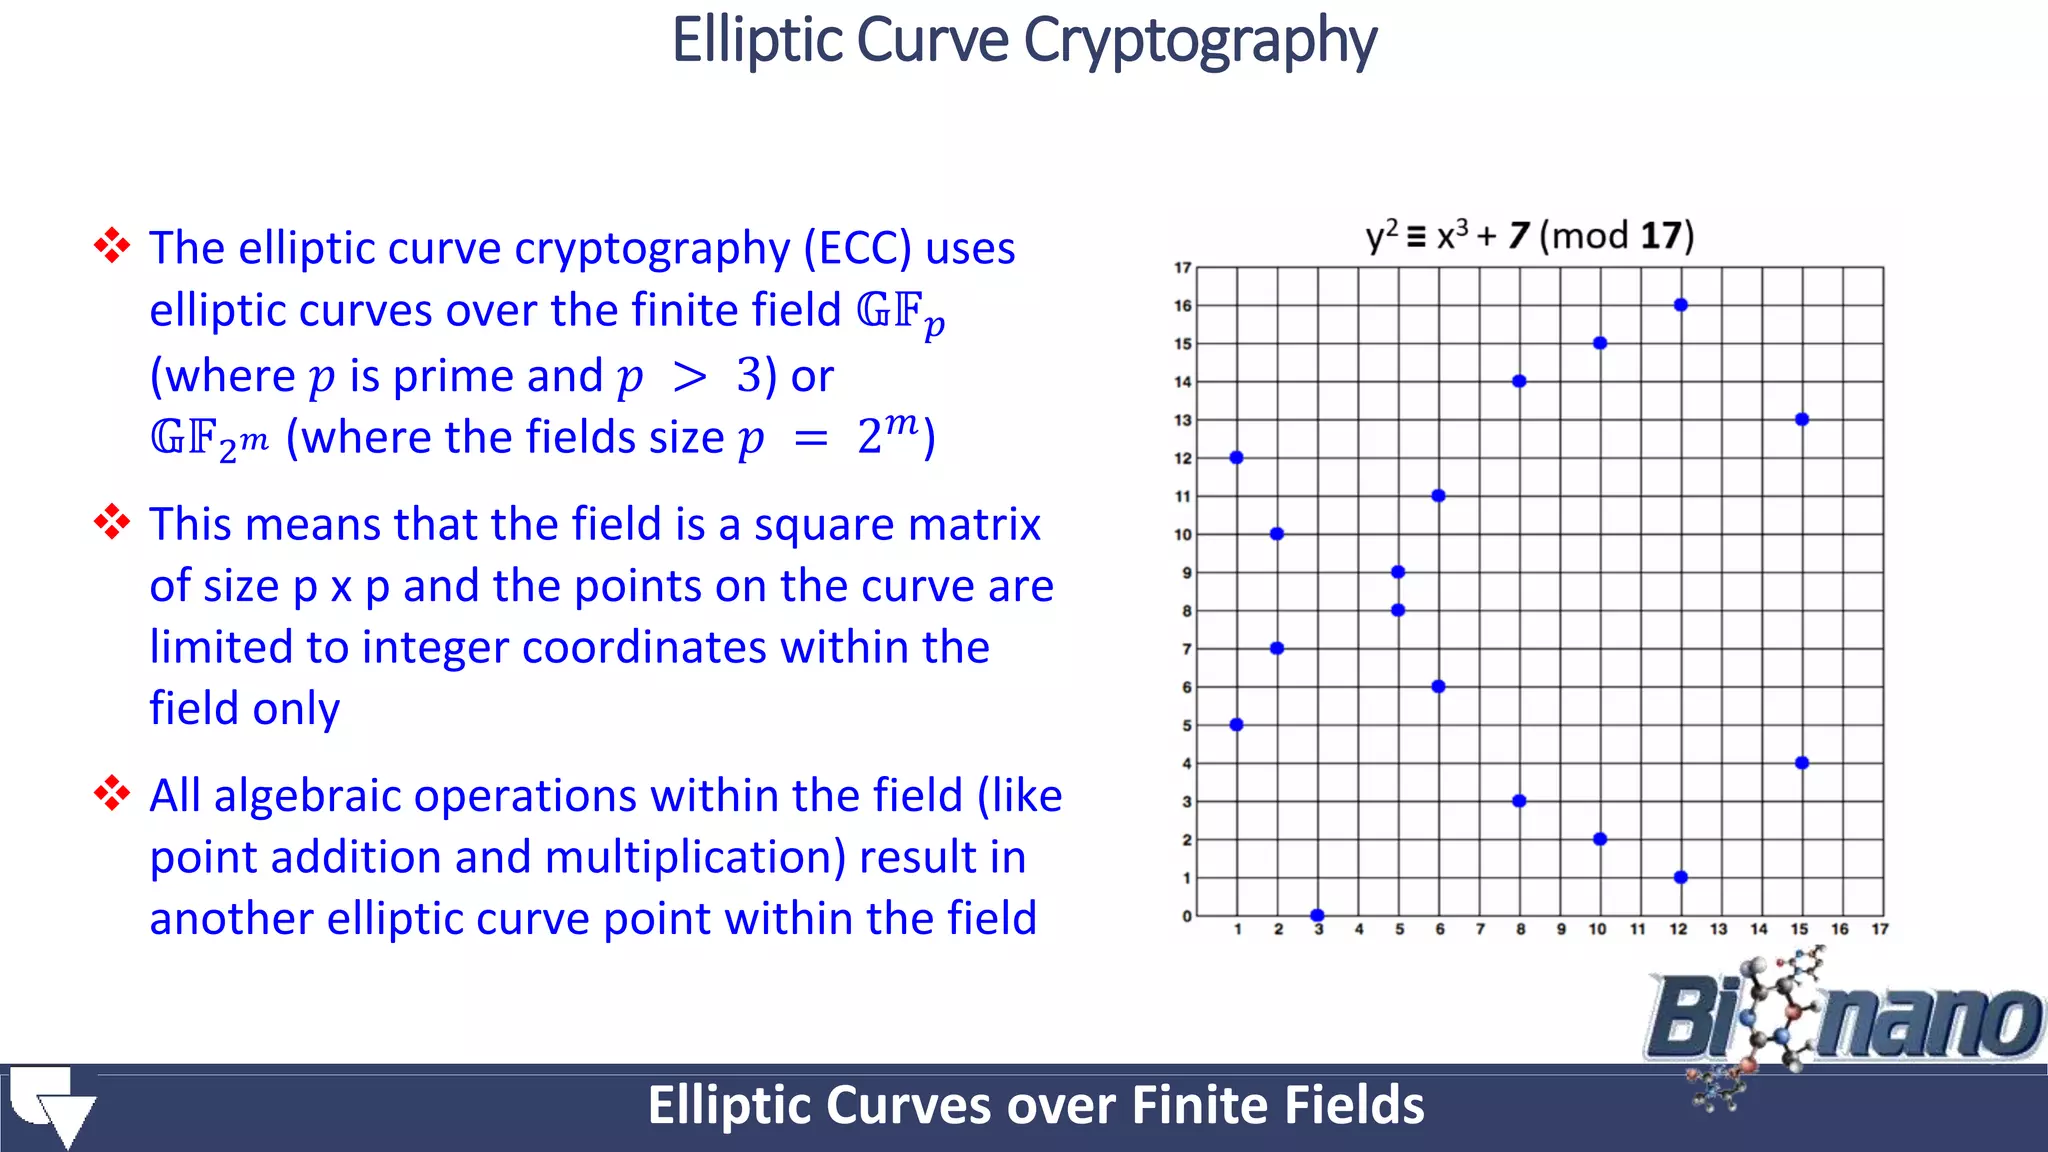
- Let’s get into particulars in regards to the elliptic curves over finite fields.
Sectigo’s Q.U.A.N.T. technique provides a clear framework to information this process, serving to businesses quantify their cryptographic footprint, uncover dangers, and assess and strategize for a secure transition. By Way Of this method, groups can navigate implementation with automated, quantum-safe solutions and monitor ongoing progress to take care of crypto agility as standards evolve. Side-channel / timing assaults are theoretically potential, and since ECC assist in many purposes is newer, the discovery of vulnerabilities in specific implementations isn’t out of the question. Signal one block of knowledge which can be verified later by others using thepublic key. Dimension (in bits) of a secret scalar for the curve (as generatedby generate_private_key()).
So through the use of a main quantity because the modulus, you possibly can guarantee that each number within the finite field will have a multiplicative inverse (or a “division” operation). three.The two panels of Supported Ciphers and Chosen Ciphers are displayed. Supported ciphers has the entire record of ciphers supported for the chosen SSL or TLS version. The under determine shows the two panels (Supported Ciphers and Selected Ciphers). Observe that the Selected Ciphers and Supported Ciphers List https://child-clothes.info/smart-tips-for-finding-7/ will also be displayed for all Preset like PFS or SuiteB or Medium or High.
Now, there are options to change different SSL/TLS variations and different encryptions within the Outbound SSL Settings. RSA is also slower than DSA when it comes to key generation, but since keys are generated as soon as and used for months or years, this is usually not an necessary consideration. The PKI Consortium brings collectively leading organizations committed to reliable digital identities and safe communication. Cryptography.exceptions.InvalidSignature – If the signature doesnot validate.
دیدگاهتان را بنویسید